About Bryan
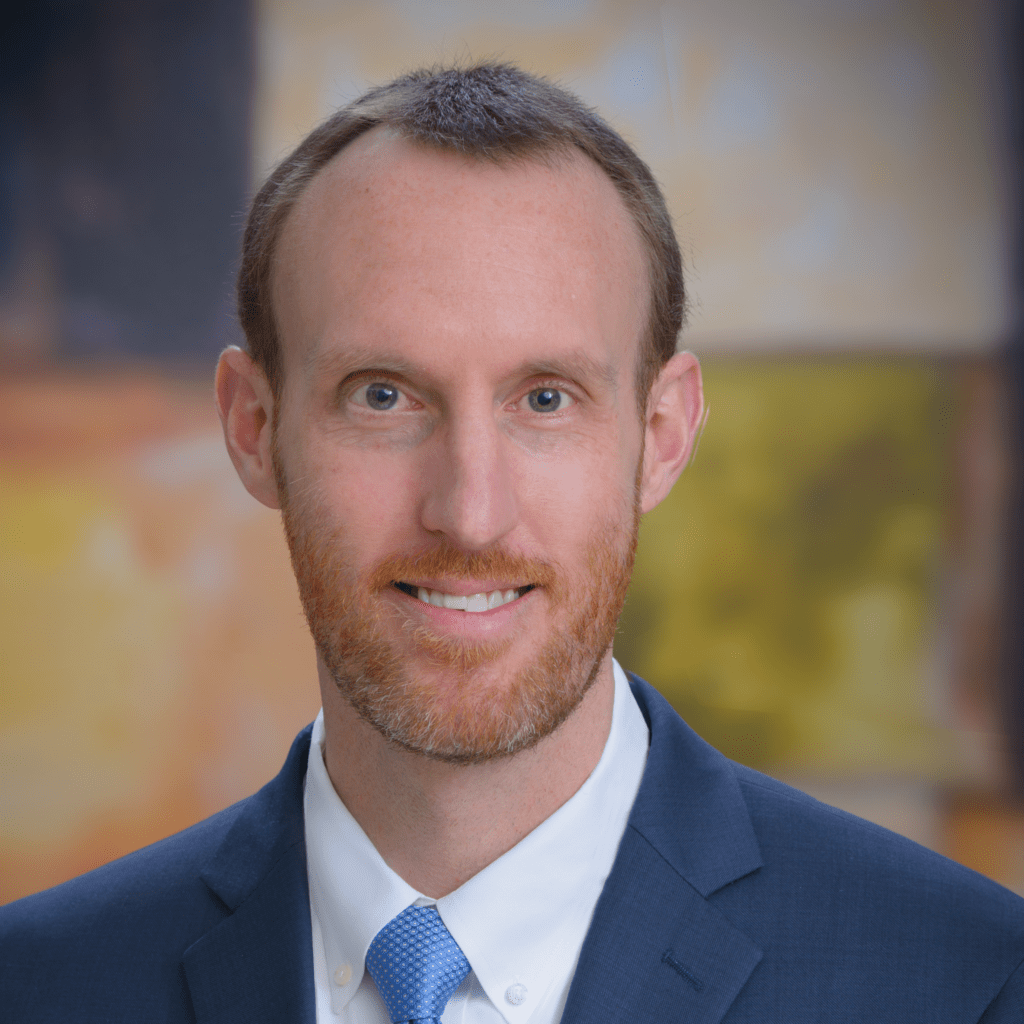
Bryan is a valued member of the Barnes Dennig family who earns high marks for his industry knowledge and dedication to his clients. He complements that professional experience with extensive technical training and education, much of which is focused on information technology and advanced accounting and audit issues.
Bryan has earned the designation of Certified Information Systems Auditor (CISA). He is a leader in the firm’s Service Organization Controls (SOC) and IT Controls practice, where he performs systems auditing, technology development, and consulting for clients, including SOC, PCI, HIPAA, and other federal and local compliance standards. A natural speaker and educator, Bryan is a regular in the firm’s Ask the Experts SOC Reporting video series, where he enlightens audiences on SOC reporting and related topics.
As a member of the firm’s Assurance Quality Control Committee, he plays a key role in ensuring clients receive the highest-quality assurance services, fostering trust and peace of mind. His broad expertise in accounting and auditing, combined with years of experience and training, makes him a valuable asset to both clients and peers, who appreciate his insight, skill, and upbeat attitude.
He’s actively involved in the community, serving on the United Way of Greater Cincinnati Agency Audit Review Committee, where he helps the organization maintain accountability for donor investments and supports the program investment process.
Bryan graduated from The Ohio State University with a Bachelor of Science and Business Administration in Accounting. He is a member of the American Institute of Certified Public Accountants (AICPA), the Ohio Society of CPAs (OSCPA), and the Information Systems Audit and Control Association (ISACA).
Education
The Ohio State University
Columbus, OH
Membership
Speaking Engagements
What Type SOC Report Do You Need?
Getting Started with SOC Reporting
SOC Reporting Readiness & Gap Assessments
SOC 2+ Reports | What They Are and How They Work
SOC Reporting for PE-Owned Companies
SOC Reporting for Data Centers
Working with the Barnes Dennig SOC Team
DIY SOC Reporting #2 | Description Criteria
DIY SOC Reporting #3 | Sub-Service Organizations
DIY SOC #4 – Which Type of SOC Report Is Right for You?
DIY SOC Reporting #5 | Section 5 of the SOC Report
DIY SOC #5 | SOC Report Section 5
DIY SOC #6 | SOC Reporting Security Criteria
Can SOC Audits Be Conducted Remotely?
How SSAE 21 Impacts Your SOC Report
Why You Shouldn’t Use Spreadsheets for Lease Accounting
HECVAT – What It Is and Why It Matters
Thrive: Non-Profit Success Stories #3 | Careers
Supplying Success to Distributors: Benchmarking Study Results Revealed