About Robert
“Our clients sleep better when their operations are safer, more efficient, and in compliance. When that’s the case, their whole business runs with more confidence.”
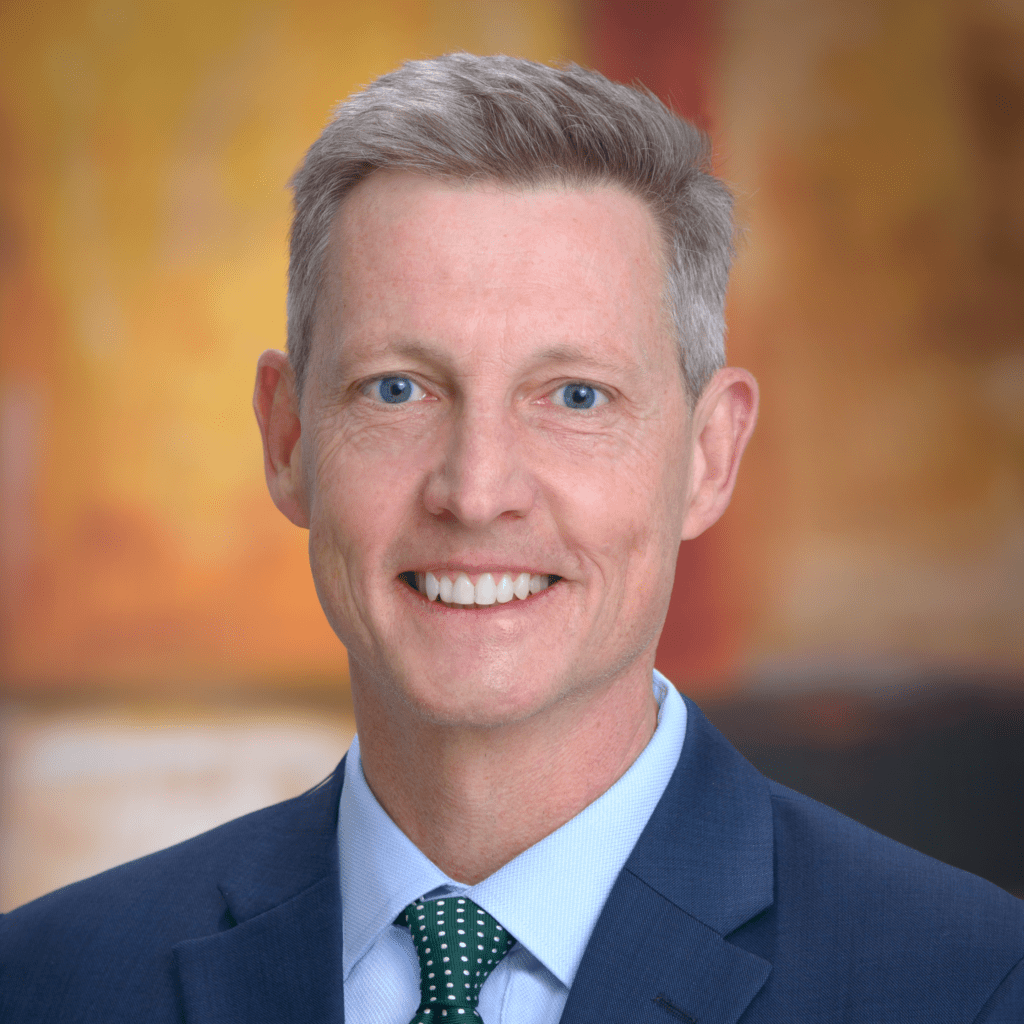
Robert leads our Risk Management practice, offering System and Organization Controls (SOC) and data security services, and his deep experience in technology consulting and audit services helps organizations of various sizes across multiple industries strengthen their internal controls and provide peace of mind to their customers and prospects. Before joining Barnes Dennig, he managed an Information Systems Risk Management practice for an international CPA firm.
In addition to being a CPA, Robert has earned the designation of Certified Information Systems Auditor (CISA) and Certified Information Technology Professional (CITP). He has extensive experience helping enterprises manage risk through technology audits and service organization controls (SOC) reporting.
In 2025 and 2026, Robert was named to Forbes’ Best-in-State CPAs List, alongside eight other standout directors from Barnes Dennig who have all made a strong positive impact on the profession and our community.
He is a former member of the FBI’s InfraGard and has been deemed a peer review program SOC Specialist by the AICPA – one of the first professionals in Ohio to earn the designation, which enables him to work as a quality control inspector for other CPA firms and the AICPA.
Robert is passionate about and deeply respected in the SOC reporting and information security field. His expertise includes PCI, HIPAA, HITRUST, SOC, and GDPR compliance: in addition to being an instructor for the AICPA’s SOC School, where he trains other organizations on key aspects of planning, executing, and reporting on SOC for service organizations, he drafted the first HMIS attestation guide. A regular contributor to Barnes Dennig’s Ask the Experts SOC Reporting video series, he helps companies understand the ins and outs of SOC reporting, including what they need to get started, the power of readiness assessments, and the different types of SOC reporting.
With his wide range of expertise in the space, Robert has helped improve information systems for large-scale public companies like Apple and small local non-profits using QuickBooks.
Robert graduated in 1992 with Distinction from Indiana University, earning a B.S. in Accounting and a concentration in Sociology. He is a frequent presenter for the AICPA and ISACA, and has served on many local boards of directors, including formerly serving as president of the Cincinnati Chapter of ISACA. He’s also participated in the HITRUST Academy. In 2026, Kennedy Heights Arts Center honored him with the Kennedy Award for his longtime leadership, financial stewardship, and commitment to helping the arts organization grow and thrive.
When he’s not helping clients develop greater peace of mind by identifying and mitigating risks, he loves traveling with family and friends. When he’s not doing that, he tries to be mindful not to overshare his excitement for his local soccer team, pickleball, latest read, or new favorite podcast (his current top picks include Hard Fork, Total Soccer Show, and Smartless).
Membership
Speaking Engagements
AI and Your SOC Report | What You Need to Know Now
What Type SOC Report Do You Need?
SOC Reporting Basics | What Do You Need to Get Started?
SOC Reporting Readiness Assessment & Gap Analysis
SOC 2+ Reports | What They Are and How They Work
Working with Barnes Dennig’s SOC Reporting Team
SOC Reporting for PE-Owned Companies
SOC Reporting for Data Centers
Cybersecurity Careers | SOC Reporting
SOC 3 Reports | What They Are and How to Use Them
Barnes Dennig Ask the Experts Series | SOC Reporting
SOC Readiness Assessments – Barnes Dennig Ask the Experts
DIY SOC Reporting #2 | Description Criteria
DIY SOC Reporting #3 | Sub-Service Organizations
DIY SOC #4 – Which Type of SOC Report Is Right for You?
DIY SOC Reporting #5 | Section 5 of the SOC Report
DIY SOC #6 | SOC Reporting Security Criteria
Can SOC Audits Be Conducted Remotely?
How SSAE 21 Impacts Your SOC Report
Let’s Talk Technology for ESG Measurement
Cybersecurity: How to Protect Your Non-Profit and Donors
Cybersecurity for Non-Profits – Tools, Strategies & Resources
SOC Reports – 3 Things You Need to Know – Ohio CPA Firm
SOC 2 and SOC Plus | Ask the Experts | Barnes Dennig
SOC Reporting Careers – Unlocking the Power of Certifications
HECVAT – What It Is and Why It Matters
The Risk of Ransomware – And How to Fight Back
Navigating Risk: A Panel Discussion
How GDPR Changes the Way You Do Business in the EU
Barnes Dennig at Pondurance Winter 2018 Quarterly Security Briefing
2019, November 19 – ISC2 Cincinnati – SOC 2 Security Reporting
2019, April 2 – ISACA Cincinnati – The Risk Assessment Landscape
2018, August 8 – Cincinnati Business Courier – What every leader should know about Cybersecurity
2018, June 10 – Kentucky Captive Insurance Association – Cybersecurity and the CEO
2018, March 21 – Xavier University Undergraduate Accounting Society – “Playing the Lottery with SOC reports”
2018, February 27 – Barnes Dennig Technology Seminar – General Data Protection Regulation (GDPR)
2018, February 12 – Pondurance Quarterly Security Briefing – SOC Reports and Third Party Vendor Management
2017, December 13 – Greater Cincinnati Planned Giving Society – Technology Update
2017, November 7 – ISACA Cincinnati – Ransomware
2017, September 13 – Butler University – Barnes Dennig and Huntington Bank – Not-for-profits and Cybersecurity
2017, May 1 – FBI, SALIX, Stock Yards Bank, Barnes Dennig – Cybersecurity Update
2017, March 22 – ISACA Northwest Ohio Chapter – CyberSecurity Nexus Fundamentals (CSX) Review Program, and Dinner Presentation on Technology Security
2017, February 22 – Leadership Council for Nonprofits – What an Executive Director/Nonprofit CEO Needs to Know About Technology
2016, September 25 – Allinial Global Webinar – Payment Card Industry Data Security Standards – (PCI DSS) Compliance Basics
2016, April 5, ISACA Cincinnati Chapter at the Original Montgomery Inn, – Third party vendor management – lessons from HIPAA and the Office of the Comptroller of the Currency
2016, April 14 & 15, ISACA and the University of Cincinnati – CSX, Cybersecurity Exam Preparation
2015, August 24, IIA, ISACA, GRC Conference, Phoenix, AZ – A study comparing HIPAA and OCC third-party vendor management guidelines
2015, August 7, OH, KY, IN Treasurers Association Conference – What the Treasurer Needs to Know about Data Security and Fraud Risks
2015, November 17 – Cincinnati Chamber of Commerce, CFO Round Table
2015, July 9 – AICPA Webinar – Center for Plain English Accounting – Information Technology Risks and Electronic Banking
2014, October 9 – Leadership Council of Human Services Executives – What an Executive Director / Nonprofit CEO Needs to know about Technology in 4Q2014
2014, December 2 – Barnes Dennig NFP Seminar – Don’t Get Caught in the Headlines – What the Nonprofit C-Suite Needs to Know About IT & Fraud
2014, March 5 – Barnes Dennig Manufacturing Seminar – Manufacturer’s Technology Update and the Digital Supply Chain
2014, April 29 – Ohio Society of CPAs – Auditing Information Technology : IT Controls in Financial Statement Audits and Internet Banking Controls
2011, September 28 – Ohio Society of CPAs – Governance for Not-for-Profits, 2011, September 28 – Ohio Society of CPAs – Internet Safeguarding
2010, September 3 – Ohio Society of CPAs – Documenting and Understanding Controls over Information Systems
2010, June 8 – Ohio Society of CPAs – What’s New in Documenting and Understanding Controls over Information Systems